Safety and non-destructive defaults
Every guarantee OrgBolt makes about what it will and will not do to your Salesforce org.
Security overview
The principles
OrgBolt is a tool that writes production Salesforce metadata. It has to be safe by default or it has no business existing. Two principles shape every feature.
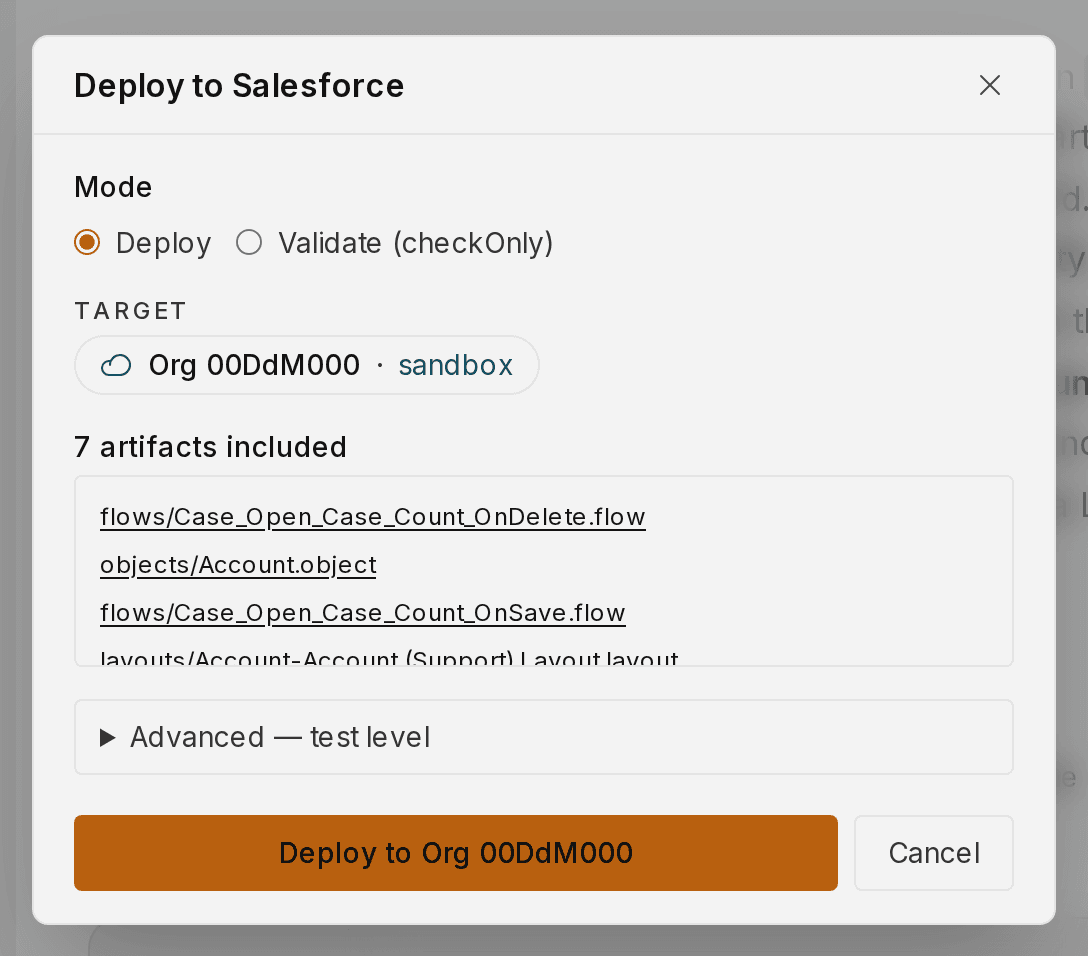
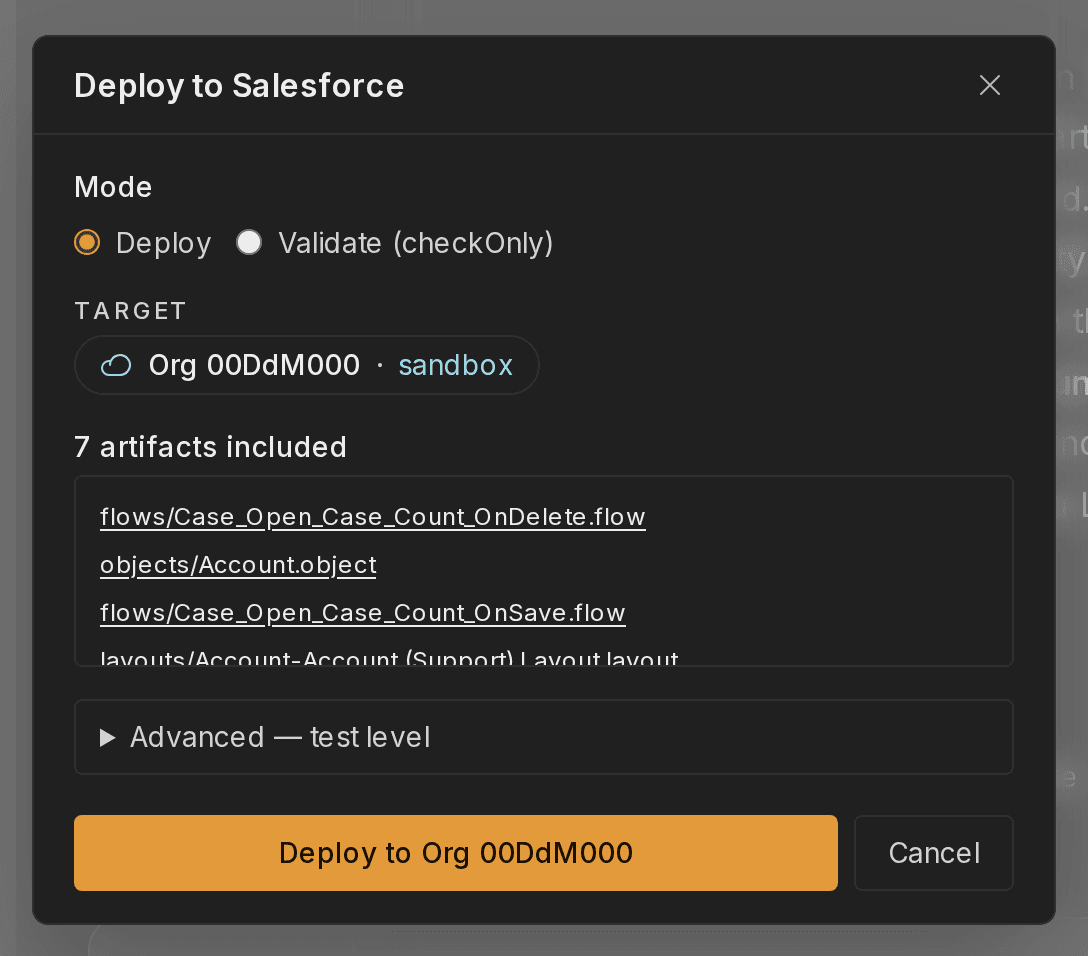
- Nothing touches your org until you click. Work is read-only. Deploy is the only phase that writes, and Deploy always asks.
- Validate before you commit. For production, Deploy defaults to checkOnly validation so you can see every error a real deploy would hit without committing anything.
The guarantees
Specifically, OrgBolt commits to the following — not as policies, but as enforced behaviors you can verify in the code and in your Salesforce audit trail.
- Work can read your org via describe calls. It cannot write, update, or delete. The OAuth scope OrgBolt asks for includes write, but the Work phase never invokes a write endpoint.
- Work can read dependent components to update them in the same task. Work never calls any write endpoint.
- Deploy on a production org defaults to Validate. If you click Deploy on production without having run Validate first in the same conversation or a prior sandbox deploy, Deploy refuses and asks you to validate first.
- Flows always deploy as Draft (status=Draft). OrgBolt will never auto-activate a flow in the same step that creates it. Activation is a manual step you perform in Salesforce Setup after reviewing the new version.
Audit trail
Every deploy is logged in two places. First, Salesforce's own Setup → Deployment Status — the same audit trail you'd see from an SFDX deploy. Second, OrgBolt's audit_log table, scoped to your workspace, which records the task, the org, the user who clicked Deploy, the deploy ID Salesforce returned, and the final status. Audit logs are retained for 7 years (anonymized after account deletion for compliance).
OAuth token security
Salesforce OAuth tokens are encrypted at rest via Supabase Vault (pgsodium) before they're written. OrgBolt decrypts a token only at the moment it needs to make a Salesforce API call, and the decrypted value never leaves the server process. Tokens are revoked via Salesforce on account deletion and cleared from the database when you disconnect an org.